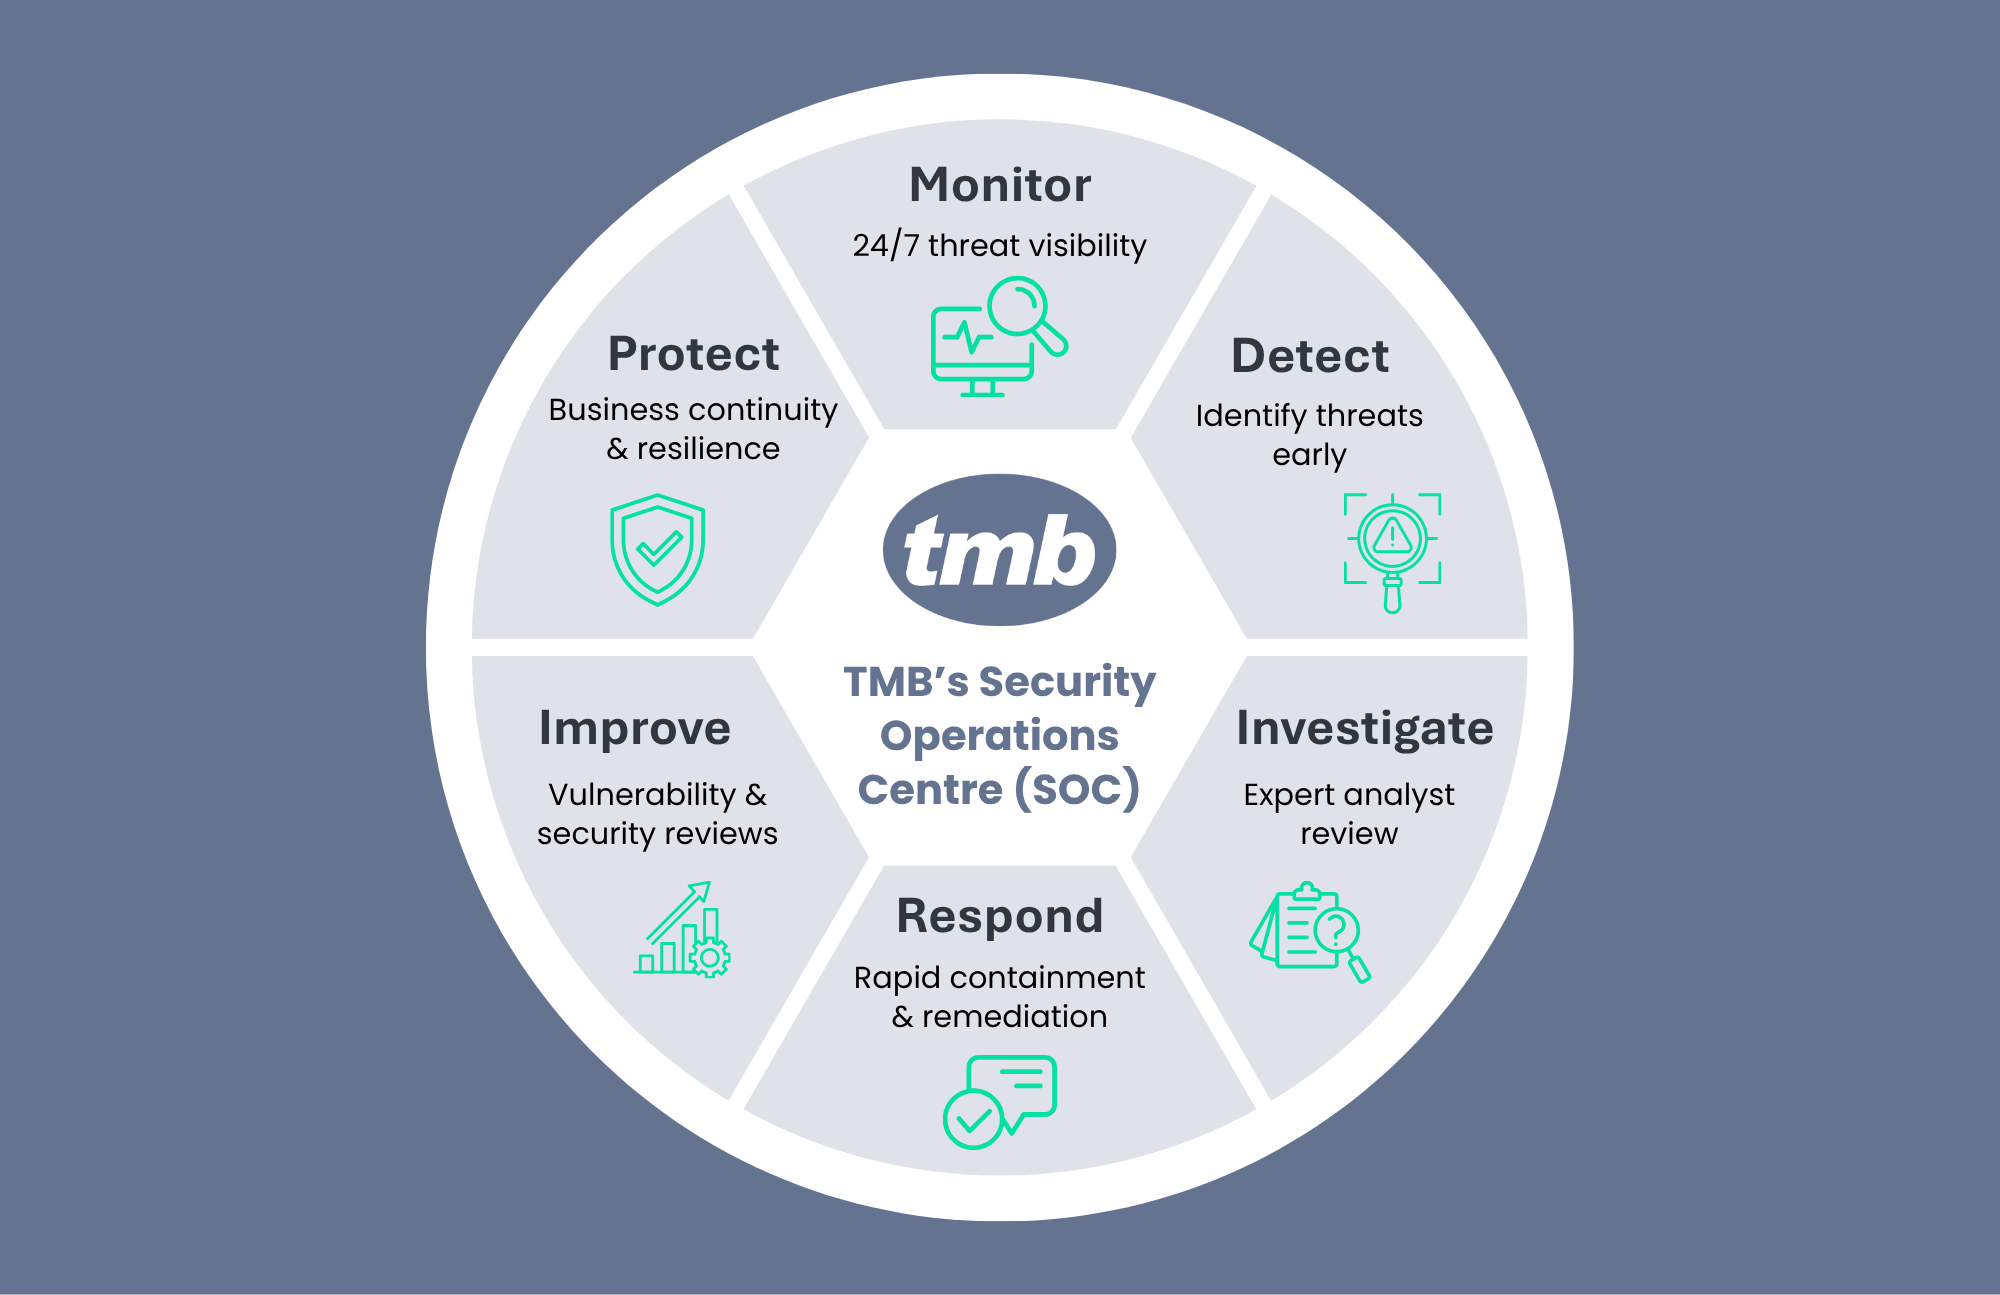

What is a Security Operations Centre?
A Security Operations Centre (SOC) is a dedicated cyber security function responsible for protecting an organisation’s IT environment through continuous monitoring, threat detection, investigation and incident response. A modern SOC combines skilled security professionals, established processes and advanced security technologies to identify, analyse and respond to cyber threats in real time.
Acting as the central hub of an organisation’s cyber defence strategy, a SOC provides visibility across networks, endpoints, cloud services, email platforms, applications and security infrastructure. Its purpose is not only to respond to threats, but also to improve security posture through proactive monitoring, vulnerability management, threat intelligence, testing and continuous improvement.
At TMB, our 24/7 Security Operations Centre provides continuous protection for customer environments, helping organisations identify risks earlier, reduce incident response times and strengthen resilience against cyber threats. TMB’s SOC acts as a centralised cyber defence function, providing around-the-clock visibility and oversight across the environments we manage. Our team monitors security events, investigates suspicious activity, identifies vulnerabilities and responds to incidents as they occur.
TMB’s SOC Team
Our Security Operations Centre is built around a team of security professionals responsible for protecting customer environments 24 hours a day, 365 days a year.
Our analysts continuously monitor customer environments, investigate suspicious activity and coordinate incident response activities when threats are identified. The team combines human expertise with advanced security technologies to reduce risk, minimise disruption and support business continuity.
Through ongoing training, threat simulation exercises, collaboration with technology vendors and access to threat intelligence, our analysts remain focused on identifying emerging risks and strengthening customer security posture.
Core Functions
- Continuous Monitoring & Detection
Our SOC provides 24/7 monitoring of customer environments, including endpoint devices, networks, cloud services, email platforms and security infrastructure.
The team analyses security events, log data, network activity and threat intelligence sources to identify suspicious behaviour and potential indicators of compromise. Through continuous monitoring, our analysts establish a clear understanding of normal activity and can quickly identify anomalies that require investigation.
- Threat Detection & Investigation
Security alerts are investigated and validated by our analysts to determine whether they represent genuine threats or false positives.
This includes:
- Malware and ransomware investigations
- Suspicious login activity
- Credential compromise detection
- Email security incidents
- Network anomalies
- Endpoint compromise investigations
- Threat intelligence correlation
Our analysts work to separate genuine threats from background noise, ensuring the most critical incidents receive immediate attention.
- Threat Hunting
Threat hunting involves proactively searching customer environments for indicators of compromise, unusual behaviours and emerging threats that may have bypassed automated controls. Using a combination of threat intelligence, behavioural analysis and security expertise, our team actively searches for risks before they develop into security incidents.
- Incident Response
When a security incident is identified, our SOC follows established response procedures designed to contain, investigate and remediate threats as quickly as possible.
Response activities may include:
- Endpoint isolation
- User account containment
- Firewall rule updates
- DNS protection updates
- Threat eradication activities
- Recovery coordination
- Post-incident reporting
Our objective is to minimise the impact of security incidents while supporting a secure and efficient recovery process.
- Vulnerability Management
Identifying vulnerabilities before they can be exploited is a critical part of maintaining a strong security posture.
Our SOC performs vulnerability scanning, risk assessment and remediation tracking to help customers understand where weaknesses exist within their environments. Findings are prioritised according to risk and business impact, supporting informed remediation decisions and reducing the overall attack surface.
- Reporting, Visibility & Compliance
Our customers benefit from security reporting, operational dashboards and ongoing review processes that provide insight into threats, vulnerabilities, incidents and security trends.
Our SOC also supports organisations working towards compliance objectives, including security frameworks and industry standards through documented processes, reporting and audit-ready evidence.
Team Structure & Key Roles
Security Analysts
Security Analysts act as the first line of defence within the SOC. They monitor security events, investigate alerts, triage incidents and coordinate containment activities where required. These analysts provide continuous oversight of customer environments and represent the frontline of cyber defence.
Threat Hunters
Threat Hunters focus on identifying advanced threats and hidden malicious activity that may not trigger traditional alerts. Through proactive investigation and analysis, they help uncover risks before they become significant incidents.
Security Engineers
Security Engineers are responsible for maintaining and optimising the technologies that support security operations. This includes implementing security solutions, fine-tuning controls and ensuring security platforms continue to operate effectively.
Incident Responders
Incident Responders lead the containment, investigation and remediation of active security incidents. They coordinate technical response activities and help ensure effective recovery following a cyber event.
SOC Leadership
SOC leadership provides strategic oversight, governance, escalation management and continuous improvement across the security operation, helping ensure customers benefit from a mature and effective security service.
Technologies & Platforms
Our SOC monitors and manages a broad range of security technologies, providing coverage across endpoint, network, cloud and user environments.
Key areas include:
- Endpoint Detection & Response (EDR)
- Managed Detection & Response (MDR)
- Security Monitoring & SIEM Technologies
- Firewall Security Management
- DNS Security & Filtering
- Email Security & Phishing Protection
- Vulnerability Management
- Dark Web Monitoring
- Security Awareness Training
- Penetration Testing
- Threat Intelligence Services
- Breach & Attack Simulation Platforms
These technologies work together to provide layered protection and enhanced visibility across the environments we manage.
Risk-Based Security Operations
Many IT support services operate primarily against service level targets.
Our SOC adopts a risk-based approach.
Security events are assessed according to:
- Threat severity
- Business impact
- Attack surface exposure
- Likelihood of compromise
This ensures critical security incidents receive immediate attention, regardless of standard operational priorities. By focusing resources where risk is greatest, we can respond more effectively to genuine threats while reducing unnecessary noise and alert fatigue.
The Value of a Dedicated SOC
For many organisations, building and maintaining an in-house Security Operations Centre is difficult, requiring specialist skills, dedicated resources and investment in multiple security technologies. TMB’s SOC provides access to that expertise through a single, coordinated cyber security function, combining continuous monitoring, threat detection, incident response, vulnerability management and security oversight.
For hotels, access to a dedicated security team can be invaluable. Our analysts work around the clock to identify threats, investigate suspicious activity and respond to security events, helping customers reduce risk, strengthen resilience and maintain confidence in their IT environment. Having the right people, processes and technologies in place is essential. TMB’s Security Operations Centre provides the expertise and operational capability needed to help organisations stay secure, resilient and prepared for the challenges of modern cyber security.
To find out more about TMB’s Security Operations Centre and how it can support your organisation, contact our team.
- info@tmbsystemsgroup.com
- 01202 818888
- www.tmbsystemsgroup.com